
Updated October 9th 2026
Risk management is a systematic process for identifying, analyzing, evaluating and treating risks that could affect an organization's objectives. The aim is to reduce the likelihood and consequences of unwanted events, but also to seize opportunities. The international standard for risk management is ISO 31000.
In this article we explain what the risk management process looks like, how a risk matrix works, the ways you can treat a risk and how to get started with more proactive risk work.
What is a risk?
ISO 31000 defines risk as the effect of uncertainty on objectives. A risk can therefore be both negative and positive, but in practice risk management is mostly about preventing unwanted events. A risk is usually described in two dimensions: how likely it is to occur and how severe the consequence would be if it did.
ISO 31000 – the framework for systematic risk management
ISO 31000 describes how organizations can work systematically and in an integrated way with risk management. The standard is not certifiable; it serves as guidance. It is built on eight principles, including that risk management should be integrated, structured, customized and inclusive:
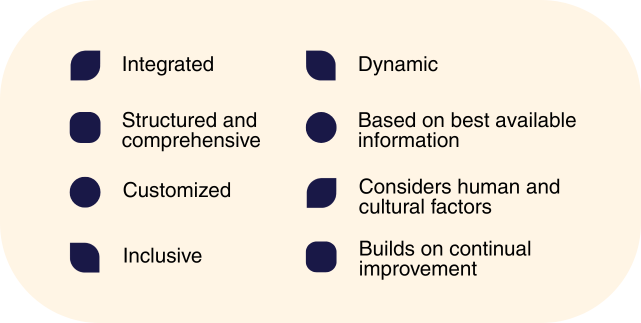
The core message of the standard is that the purpose of risk management is to create and protect value. Risk management is therefore not a side process, but part of governance, culture and decision-making.
The risk management process step by step
ISO 31000 describes a process made up of the following parts:
- Communication and consultation. The people concerned are involved throughout, so that the risk picture is based on real knowledge of the operations.
- Scope, context and criteria. You define what the risk assessment covers and which criteria determine whether a risk is acceptable.
- Risk identification. What could happen, where and why?
- Risk analysis. How likely is it, and how serious would the consequences be?
- Risk evaluation. The results are compared against the criteria to decide which risks need treatment and in what order.
- Risk treatment. Actions are selected and implemented.
- Monitoring and review. Risks and actions are followed up continuously, because conditions change.
- Recording and reporting. The process and its results are documented and reported to decision-makers.
Steps 3–5 together are called risk assessment.
How a risk matrix works
A risk matrix is a common tool for analyzing and prioritizing risks. Likelihood and consequence are each rated on a scale, often 1–4 or 1–5. The risk score is calculated by multiplying the two. A risk with likelihood 4 and consequence 5 gets a score of 20, while a risk with likelihood 2 and consequence 2 gets a score of 4.
The matrix is then divided into zones, for example green (acceptable), yellow (act if needed) and red (act immediately). This makes it easy to see which risks to prioritize. Where the boundaries go is decided by the organization based on its own risk criteria.
Four ways to treat a risk
- Avoid. Refrain from the activity that gives rise to the risk.
- Reduce. Introduce measures that lower the likelihood or the consequence, such as a control, training or a new procedure.
- Share or transfer. Move part of the risk to someone else, for example through insurance or contracts.
- Accept. Consciously accept the risk because it is low or because the cost of action outweighs the benefit.
Risk management in ISO 9001 and other standards
ISO 9001 clause 6.1 requires the organization to determine the risks and opportunities that need to be addressed and to plan actions for them. Similar requirements exist in ISO 14001, ISO 45001 and ISO 27001. ISO 31000 is often used as methodological support to meet those requirements.
Risk management and non-conformance management
Risk management is forward-looking and deals with what could happen. Non-conformance management deals with what has already happened. The two are connected: a non-conformance often reveals a risk that was not adequately managed, and non-conformances are one of the most important sources when risks are identified and re-evaluated. Read more about what a non-conformance is.
Common challenges in risk management
In many organizations, risk work is an isolated activity carried out once a year in an Excel file that only a few people can access. The result is often that:
- risk management is seen as yet another requirement rather than something that helps the organization
- the organization becomes reactive rather than proactive, acting only after something has happened
- the focus is on filling in matrices rather than understanding and reducing the risks
- the risk assessment is not updated when the organization changes
Get started – 5 steps to more proactive risk management
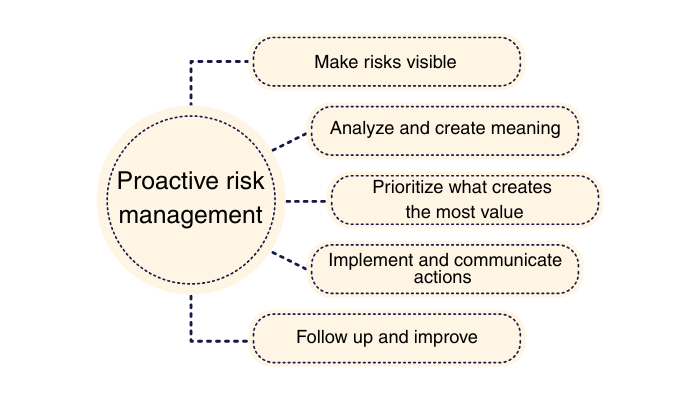
- Make the risks visible. Involve the organization in identifying risks and opportunities where they actually arise. Use non-conformances, incidents, inspections and employee dialogues as sources of insight.
- Analyze and create meaning. Assess likelihood, consequence and impact on objectives. Discuss why the risks exist, not just that they exist.
- Prioritize what creates the most value. Which risks are most critical? Which opportunities create the most value? Direct resources accordingly.
- Implement and communicate actions. Make sure responsibilities, timelines and follow-up are clear. Communicate both decisions and results.
- Follow up and improve. Risks change as the organization and the world change. Evaluate what has worked and adjust continuously.
Summary
Risk management is the process of identifying, assessing and treating what could affect the organization's objectives. ISO 31000 provides a framework for the process, and a risk matrix is a common tool for prioritizing. Risk management creates the most value when it is part of everyday work and connected to non-conformances and improvement work, not when it is done once a year.
Next step: See how Centuri works as risk management software →